Identity Challenge Card
The Identity Challenge Card is a printed grid of word pairs — no phone, no app, no network. A worker reads back a one-time coordinate and their identity resolves locally: at the service desk, at login, and at a password reset.
- Every worker, every environment
- Deployed in under an hour
- No MDM, no app, no hardware
- Multilingual — RTL and CJK included
- Easy re-enrollment — no device pairing
Read transcript
The Identity Challenge Card, from Avatier. Deviceless MFA for every worker.
Most MFA assumes a trusted device is there when someone signs in. For most of the workforce, it isn't. Eighty percent of workers are deskless. They're on factory floors, in hospitals and out in the field, and they rarely carry a work phone. So organizations write MFA exceptions for them, and those exceptions are the first thing attackers map.
The Identity Challenge Card closes that gap. It's a printed grid of word pairs. No phone, no app, no network. The system asks for a coordinate, the worker reads the matching word off the card and adds a private PIN, and their directory identity is checked automatically. Each value works only once, so it can't be replayed. And it all resolves locally, even when devices, networks or the identity provider are down.
One card covers three moments. At the service desk, the agent verifies the caller, not the caller's phone. At login, it works with or without a password, including on shared workstations and virtual desktops. And at a password reset, a locked-out worker proves who they are and resets it themselves, with no help desk call.
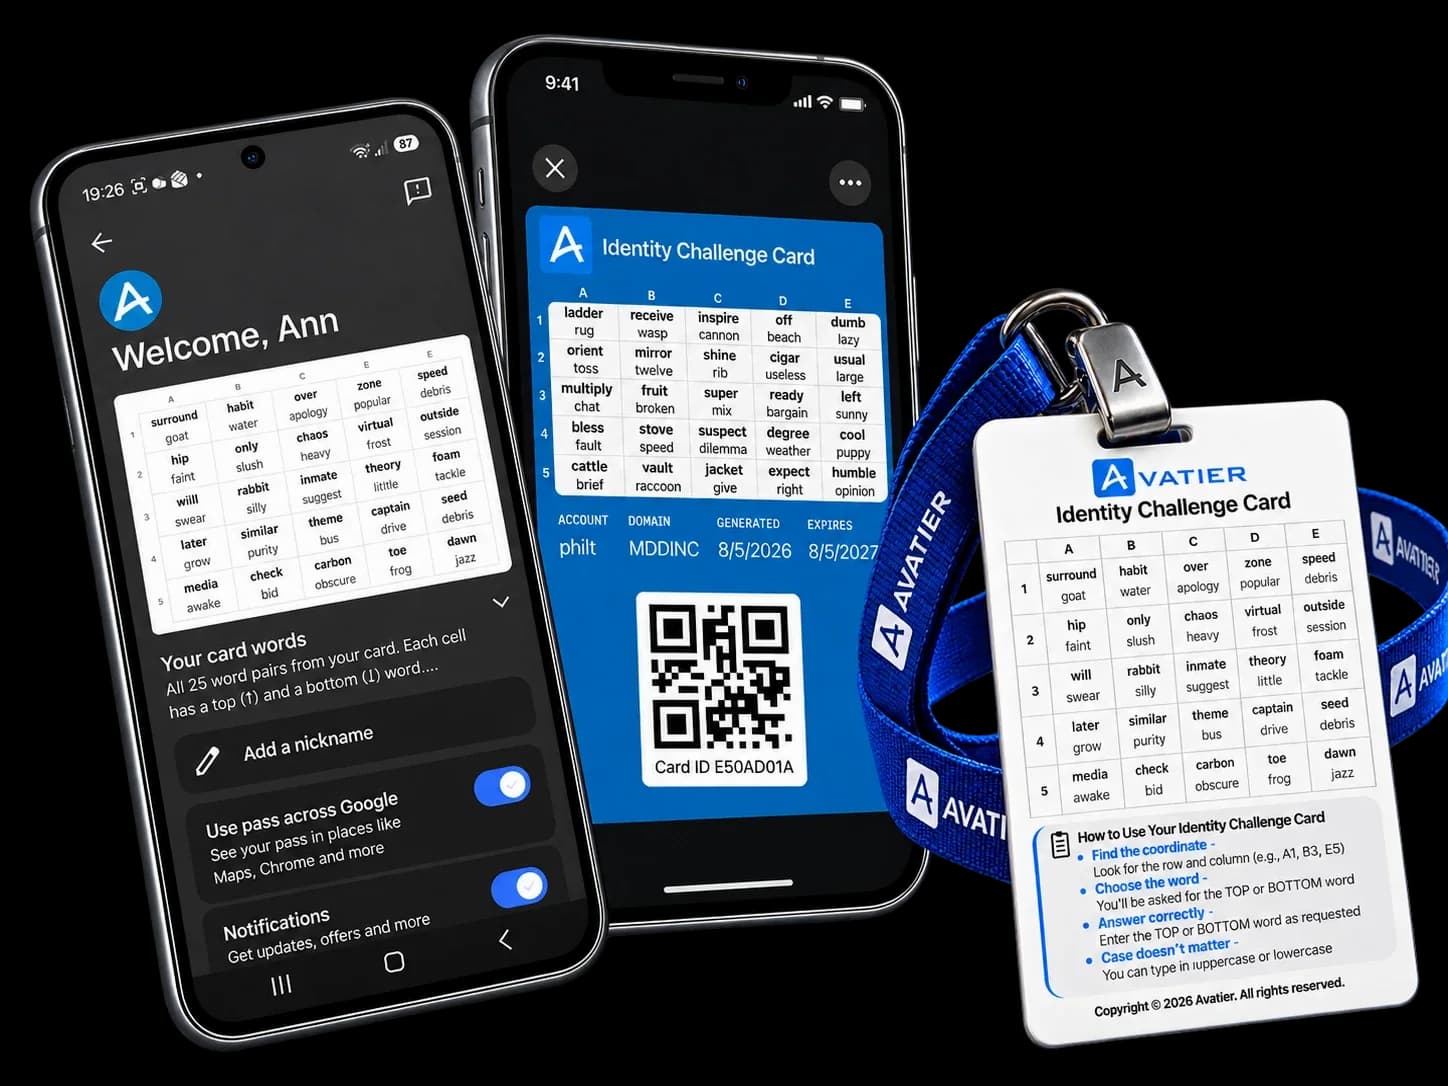
The card can also live in Apple Wallet, Google Wallet or Samsung Wallet, as a backup alongside the printed card.
Cards are issued through the identity governance workflow you already run. Every challenge and re-issue is logged, and the whole workforce can be up and running in under an hour.
Try the live card on this page, or book a meeting with the team.

Protecting the world’s workforce since 1997 • Over 15 Million Licenses Sold

Use Cases
Three Use Cases, One Printed Card
The same card covers the three moments a credential gets proven, replaced, or recovered — at the service desk, at login, and at reset. Play any explainer and follow the transcript as it speaks.
- Use Cases 01TranscriptTap a word to play from there
A caller says they're locked out and need their access back.
The agent has to decide: is this really them?
Texting a code to the caller's phone assumes the phone is theirs, not a device the attacker may already control.
The Identity Challenge Card, from Avatier, is deviceless MFA on a printed card.
The agent names a coordinate.
The caller reads the matching word back off the card.
The desk checks the answer locally.
Each value works only once, so it can't be replayed.
Security questions can be researched.
What's on the card isn't online, or on a device.
It still works when the identity provider is down.
Built for service desk leaders, and for the security and IT leaders behind them.
Verify the human, not the device.
Try the live card at identitychallengecard.avatier.com
Verify the Human
Someone calls the service desk asking for their access back. The agent names a coordinate, the caller reads the answer off their printed card, and that value is spent — a live identity check that doesn't rely on a device the attacker may already control.
See it for the service desk - Use Cases 02TranscriptTap a word to play from there
Same workstation, a different worker every shift.
The login has to know who's standing there.
Most MFA assumes a trusted device at sign-in.
On the line, there often isn't one, so those workers become exceptions.
The Identity Challenge Card, from Avatier, puts the factor on a printed card instead.
Here she signs in without a password.
A coordinate appears.
She reads the word off her card, adds her PIN, and her employee ID is checked automatically.
Same card on a virtual desktop.
Where the site keeps the password, the card answers the MFA challenge.
It sits alongside the MFA you already run, and policy routes each worker to the right method.
Built for shared workstations, frontline teams, and the IT and security leaders covering them.
Login, with or without a password.
Try the live card at identitychallengecard.avatier.com.
Login, With or Without a Password
The card is the factor either way. Use it passwordless on shared workstations and virtual desktops, or keep the password and let the card answer the MFA challenge — no phone required, no app required, no hardware token to enroll.
Compare to device MFA - Use Cases 03TranscriptTap a word to play from there
Back from break, and locked out.
The phone that should prove it's you is dead, out of signal, or in a locker.
With device MFA, that turns into a help desk call.
With the Identity Challenge Card, from Avatier, he resets it himself.
The new password field stays locked.
A coordinate appears.
He reads the word off his printed card and adds his private PIN, and his employee ID is checked automatically.
Proof first.
Only then does the password change.
The phone never came into it, and there was no help desk call.
Every challenge and re-issue is logged in the identity governance you already run.
Built for workers who can't count on a phone, and for service desk leaders tired of the lockout queue.
Proof first, then the password.
Try the live card at identitychallengecard.avatier.com.
Self-Service Password Reset
A locked-out worker resolves it themselves. The card proves who they are before the password changes, so the reset needs no help desk call — and it still works when the phone is dead, out of signal, or in a locker.
Try the live card
Also Available
Identity Challenge Card for Mobile Wallets
Human verification in your pocket. Add the card to Apple Wallet, Google Wallet or Samsung Wallet for fast access and a secure backup identity, ready when standard MFA fails — alongside the printed card, not instead of it.
- Wallet-ready access
- Human verification
- Backup MFA when it matters
- Government ID verification (coming soon)
Bring identity backup to every employee.
Device-Dependent MFA Can't Protect Workers Who Don't Have a Device
Every MFA product on the market assumes a trusted device is available at authentication time. That assumption is wrong for most of the workforce.
80% of the global workforce is deskless. Factory floors, hospitals, field service, retail, logistics, education, construction — the workers running the operation rarely carry a work phone, and the ones who do can't use it on the shop floor.
The result is a documented coverage gap. Organizations write MFA exceptions for the workers they can't reach. Those exceptions are the attack surface cyber adversaries map first.1,2,3
80 percent
80% of the global workforce is deskless
2.7 billion workers worldwide don't sit at a desk, don't carry a work phone, and can't install an authenticator app — and they're the workforce most organizations leave uncovered.
20 industries
Industries
5 to 88 percent
Device MFA reach
Deviceless MFA closes the red. Device-dependent MFA can't reach it without a phone, an app, a token, or a network.
For the CFO: every uncovered frontline worker is an uninsured breach vector — one stolen credential from a seven-figure incident, a denied cyber-policy claim, and an audit finding that pushes your next renewal. Deviceless MFA is how that math stops working against you.
Fifteen minutes. We'll map your coverage gap and what it's costing you today.
Sources
Fortune 500 workforce composition derived from 10-K filings, Bureau of Labor Statistics industry occupation mixes, and Gallup's State of the Global Workplace (2024). Deskless ratio per industry follows Emergence Capital's Deskless Workforce Report. Full methodology available on request.
- [1] Enterprise VC research — State of Technology for Deskless Workers (2020)
- [2] Global strategy consultancy — Making Work Work Better for Deskless Workers (Dec 2022)
- [3] Industry analyst firm — 75% of new mobile initiatives target frontline workers
- [4] Business publication — 2025 ranking of largest U.S. companies by revenue (June 2025)
The Iranian Handala Stryker Attack Is Why Deviceless MFA Exists.
Handala is Iran-aligned. They don't want a ransom — they want you offline.
State-aligned wiper groups don't negotiate; they build payloads designed to keep your workforce locked out. Then the phone rings at your service desk. “This is John from Cardiology — I need my access back, now.” How does the tech on the line know it's actually John — and not the attacker who already owned John's phone?
Device-Dependent MFA vs Deviceless Authentication
Device-Dependent MFA
Deviceless Authentication
With this fallback identity layer, Stryker's rebuild would have been days, not weeks.
Three Factors. Zero Device Dependency.
Deviceless MFA resolves three independent factors — all locally, all without a device, and all in under 10 seconds.
Challenge Card Factor
A printed grid of word pairs. At login, the system asks for a specific coordinate — the user reads the answer directly off the card. No network call. No device.
Private Knowledge Factor
A short PIN that only the user knows. Bound to the card via policy and verified in-memory so replay and brute-force have no surface.
Identity Anchor Factor
The user's directory identity — Employee ID, badge, or SCIM-provisioned principal. Ties the challenge to a specific human, with full audit trail.
See Deviceless Authentication. Try It. Understand It in 60 Seconds.
Self Enrollment or Auto Enroll Everyone at Once.
A narrated walkthrough of Deviceless MFA, the card, and how the three factors resolve locally.
This is Deviceless MFA. Try it.→
No signup. No download. Resolve a live three-factor challenge against a printed card, right here — same flow a worker runs during an identity outage.
No phone required
No app required
No network required
No hardware token required
No dependency on compromised systems
Works in any language, including RTL and CJK
| # | A | B | C | D | E |
|---|---|---|---|---|---|
| 1 | INSTALL POWDER | GARDEN BRIDGE | MARBLE SILVER | ROCKET WINDOW | GUITAR CASTLE |
| 2 | PLANET ANCHOR | TURTLE FOREST | BASKET TEMPLE | VELVET PIRATE | COTTON DRAGON |
| 3 | CANYON MAGNET | PUZZLE ORANGE | VIOLET BEACON | COPPER JUNGLE | CARPET MONKEY |
| 4 | HARBOR KNIGHT | VISION QUARTZ | JASPER WILLOW | SUMMIT STREAM | PARROT FABRIC |
| 5 | MEADOW COBALT | FABRIC SPHINX | FALCON BINARY | ORCHID PRISM | LANTERN OXYGEN |
Coordinate C2 — TOP word
Your PIN 1234
Employee ID EMP-48291
How Three-Factor Works
· Challenge Card Factor — Find the coordinate (e.g., A1, B3) and enter the TOP or BOTTOM word
· Private Knowledge Factor — Read your 4-digit PIN, then enter it in the PIN field
· Identity Anchor Factor — Your Employee ID is verified automatically
· All three factors required — the word and PIN must both be correct to gain access
· New challenge — Tap 'New Game' to randomize a fresh coordinate and PIN
The Business Value of Deviceless MFA Mapped to Who's Buying
Every stakeholder wins a different outcome. The Identity Challenge Card is the rare control where the CISO, CIO, CFO, CEO, service desk, and industry analyst each get their own answer.
Ready to close your compliance gaps with Deviceless MFA?
Book a 20-minute walkthrough tailored to your workforce — we'll map your exceptions to a deployment plan before you leave the call.
Built for Global Workforces
The Identity Challenge Card ships in 34 languages, including RTL Arabic and Hebrew and CJK Chinese, Japanese, and Korean. Same card, same three-factor flow — localized for every worker.
Deviceless MFA, Trusted in Regulated Environments
Designed from day one for CMMC, HIPAA, PCI-DSS, GDPR, and FERPA workloads. Three architectural pillars make the compliance story simpler than device-bound MFA, not harder.
Privacy by Architecture
Zero personal data on the auth mechanism
- No phone number, biometric, or personal data touches the card
- Card contents are opaque without the user's PIN
- Zero GDPR exposure from the authentication channel
- No third-party processor between the user and the challenge
- Revocation is immediate — no upstream device cleanup
Full Lifecycle Controls
Governed issuance, revocation, and audit
- Every card is issued through the existing IGA workflow
- Every challenge and re-issue writes an immutable audit record
- Policy-enforced expiration and re-enrollment windows
- Identity-verified re-issuance closes the social-engineering path
- Separation of duties between issuer, approver, and auditor
Replay-Proof by Design
No push, no replay, no shared secret
- No push notifications — push fatigue has no surface
- Each coordinate value is one-time — replay is structurally impossible
- Air-gapped verification — no network attack surface
- No TOTP shared secret to exfiltrate
- Offline verification with no shared secret to steal
Recognized on Gartner Peer Insights
4.4
Based on 14 verified reviews of AvatierIdentity Governance and Administration
Read the reviews on Gartner Peer Insights


Download White Paper + Product Sheets
The full category argument, the Stryker recovery narrative, and the product sheet — three PDFs for the CISO, CIO, and board packet.
Frequently Asked Questions
The same questions come up in every CISO, CIO, CFO, CEO, service desk, and analyst call. Answers below — pick your persona.
Deviceless MFA for 100% of the workforce
What exactly is Deviceless MFA — and how is the Identity Challenge Card different from every other MFA?
Is a printed card actually secure? A lost card means a compromised credential.
We already have MFA. Why does our existing solution leave a documented gap?
Can push bombing or replay attacks work against this?
See Where Deviceless MFA Fits in Your Environment
No commitment · 30-min Deviceless MFA walkthrough · same-day response
Talk to the team behind the Identity Challenge Card — the first production Deviceless MFA.
Further reading
Related from the Identity Challenge Card library
Phishing-Resistant MFA: What CISA and NIST Require and How to Deploy It in an Enterprise
Phishing-resistant MFA is the term CISA, NIST 800-63B Rev. 4, and Executive Order 14028 use for the authentication category that survives the attack patterns that defeated SMS, OTP, and push-approval MFA. The 2026 enterprise reference on what qualifies, what doesn't, and the deployment architecture across mixed workforces.
Read more
Beyond Foundational MFA in 2026: The Recovery Channel Gap
Phishing-resistant MFA is the right answer for the front door. It does not protect the recovery channel, which is where the 2026 attacks are landing.
Read more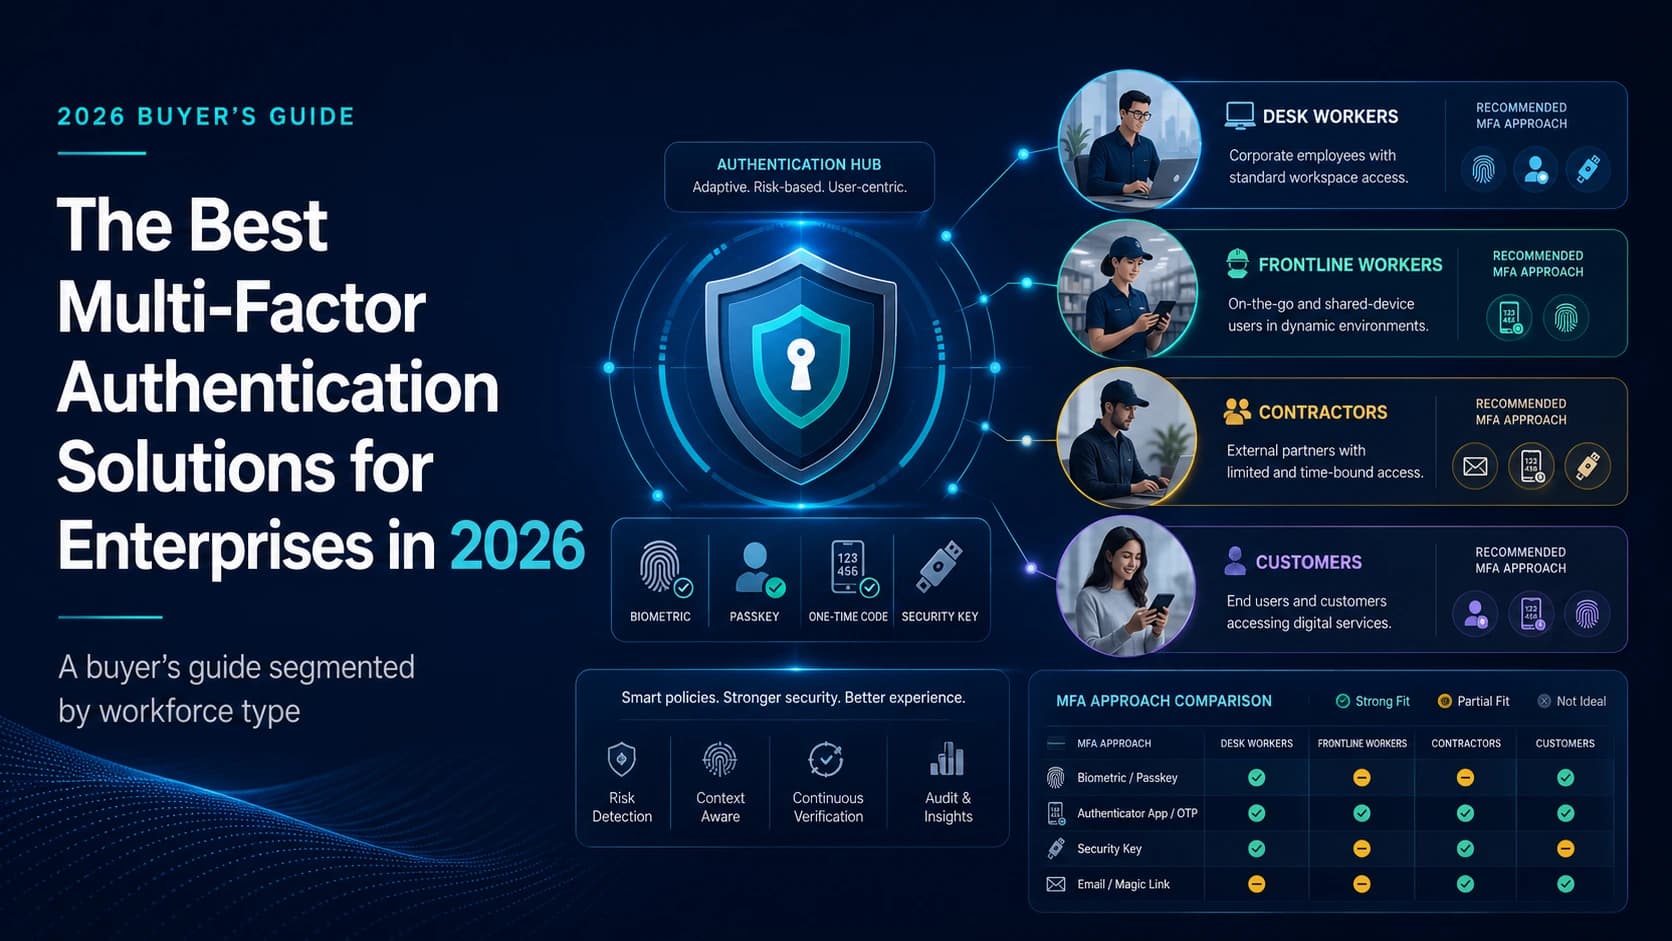
Best MFA Solutions for Enterprise in 2026, Compared by Workforce Type
A 2026 buyer's guide to enterprise MFA solutions, segmented by workforce type. Compare 12 vendors across desk, frontline, contractor, and customer use cases.
Read more