MFA for Retail Store Associates on Shared Terminals, with Avatier
How to run MFA for store associates with no company phone: Avatier's printed Identity Challenge Card at shared back-office terminals, plus PCI DSS scope, lockouts at open and seasonal hiring.
How to run MFA for store associates with no company phone: Avatier's printed Identity Challenge Card at shared back-office terminals, plus PCI DSS scope, lockouts at open and seasonal hiring.
- Retail store MFA needs a factor tied to the associate, not to a company phone they don't have or to the shared terminal.
- Avatier's Identity Challenge Card is a printed grid of word pairs plus a private PIN: no phone, no app, no network.
- PCI DSS v4.0 Req. 8.4.2 calls for MFA on all access into the CDE, with a note excluding cashier IDs that reach one card number at a time.
- Lockouts at store open are resolved with the card or with Avatier Login Reset at the Windows and Mac login screen.
- HR User Provisioning and Group Automation move seasonal hires and promotions through access changes from HR data.
MFA for retail store associates means giving every associate a second factor that doesn't depend on a company phone they were never issued, and tying each sign-in at a shared back-office terminal to a named person rather than to the machine or a store login. Avatier's Identity Challenge Card™ does that with a printed card and a private PIN: in Avatier's words, "no phone, no app, no network."
The card in one paragraph: "The Identity Challenge Card is a printed grid of word pairs." At sign-in, the system asks for a coordinate, the associate reads the matching word off the card and adds a private PIN, and their directory identity is checked automatically. "Each value works only once, so it can't be replayed." For the full frontline walkthrough, see MFA for Frontline Workers Without Phones. The rest of this post stays in the store: shared terminals, PCI DSS scope, lockouts at open, calls to the help desk and seasonal hiring.
Why store sign-ins end up on the MFA exception list
Device MFA assumes a device in the associate's hand at sign-in. Avatier names the assumption directly: "Most MFA assumes a trusted device is there when someone signs in." An associate who was never issued a company phone breaks it on the first shift.
Shared terminals add a second problem. Avatier's login explainer opens on it: "Same workstation, a different worker every shift. The login has to know who's standing there." A factor tied to the machine, or a shared store login, proves which terminal signed in, not which associate.
Without a per-person factor, the fallback is an MFA exception. Avatier names who ends up there: "device-based solutions exclude factory floors, shared workstations, field staff, and contractors." It also names the cost: "Organizations write MFA exceptions for the workers they can't reach. Those exceptions are the attack surface cyber adversaries map first." The card is meant to sit beside existing MFA rather than replace it: "It sits alongside the MFA you already run, and policy routes each worker to the right method." For example, policy could route a district manager with a company phone to an authenticator and store associates to the card.
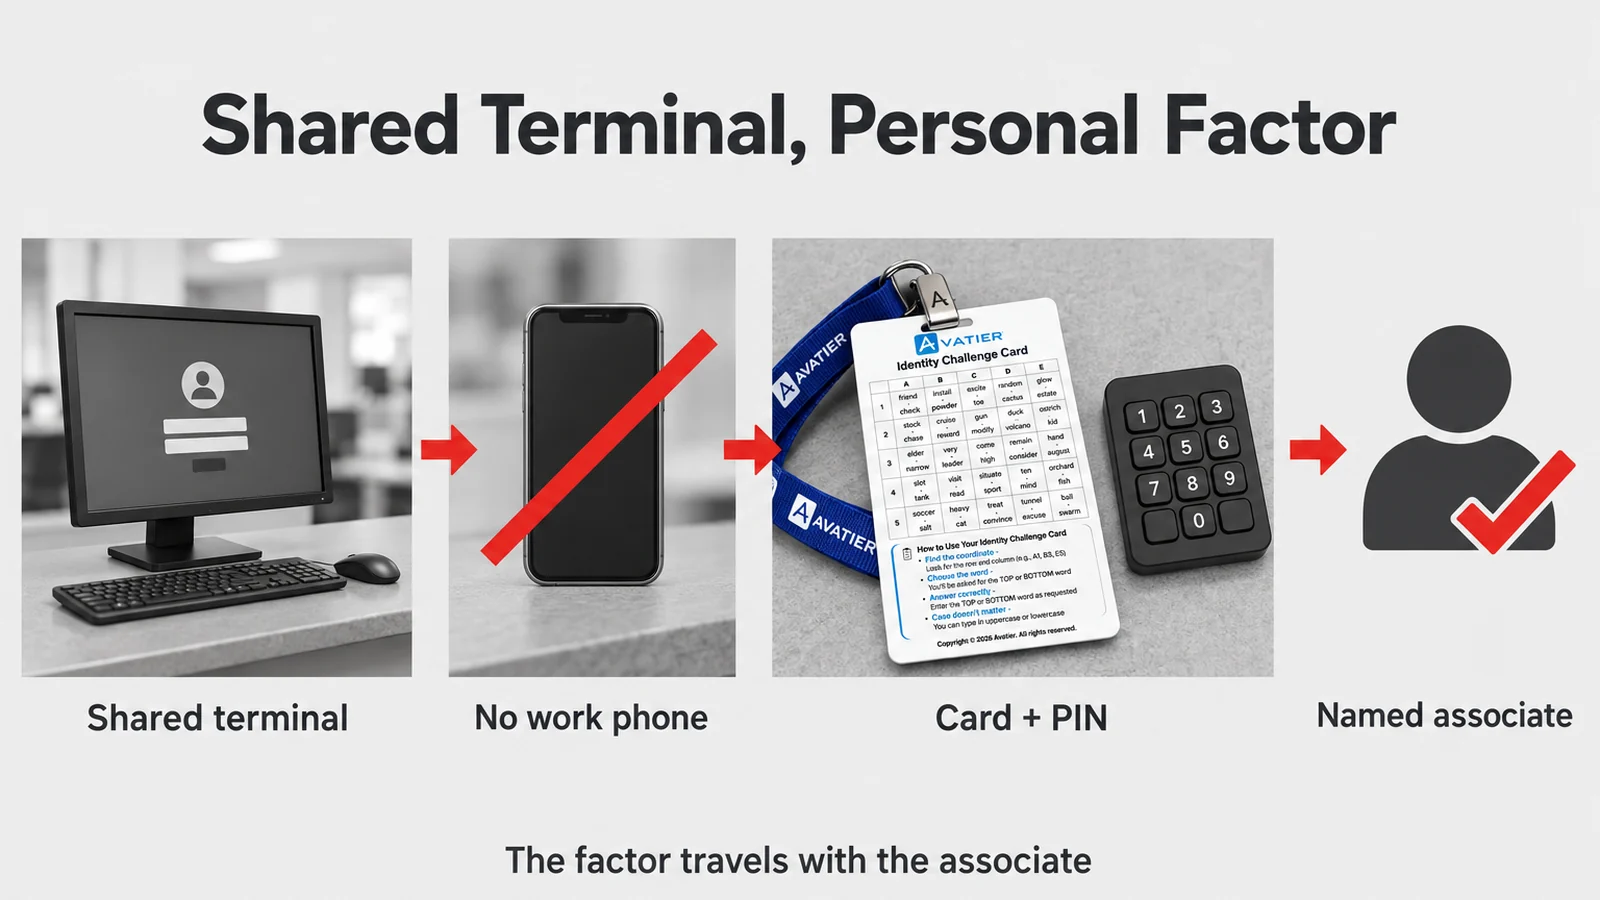 The terminal stays shared, but the second factor belongs to one associate, so every sign-in names a person instead of a store login.
What PCI DSS asks of store accounts
In the PCI DSS v4.0 requirement text, as reproduced in the PCI SSC's SAQ D for Merchants, Requirement 8.4.2 reads "MFA is implemented for all access into the CDE," and the standard marked it a best practice until 31 March 2025, required after that date. Requirement 8.2.2 says group, shared or generic accounts are "only used when necessary on an exception basis," with conditions including "Individual user identity is confirmed before access to an account is granted" and "Every action taken is attributable to an individual user." Both requirements carry a note for the register: 8.4.2 "does not apply to" user accounts on point-of-sale terminals "that have access to only one card number at a time to facilitate a single transaction (such as IDs used by cashiers on point-of-sale terminals)," and 8.2.2 is "not intended to apply" to those accounts either. The PCI SSC's FAQ 1591 adds that if a user's access to a system component "can be used to connect into the CDE, then MFA is required." As general guidance, that makes scoping the first job: list which store accounts, such as back-office, manager and key-holder sign-ins, can reach the CDE, and agree the list with your assessor. For the wider Requirement 8 picture, see PCI DSS v4 Access Control Requirements.
A store shift at a shared back-office terminal
Start by listing each store terminal type: back-office Windows or Mac workstation, virtual desktop, or register. Avatier names shared workstations and virtual desktops for the card, and the Windows and Mac login screen for Login Reset, so start with those. Then walk one shift:
- Sign-in. Avatier's login use case covers both setups: "Use it passwordless on shared workstations and virtual desktops, or keep the password and let the card answer the MFA challenge."
- A lockout at store open. With the card, "a locked-out worker proves who they are and resets it themselves, with no help desk call." On Windows and Mac terminals, Avatier Login Reset "embeds secure, MFA-verified recovery directly into the Windows and Mac login screen," and it "Updates locally cached credentials after a reset to prevent secondary lockouts when working off the corporate network." It works on "Active Directory–joined, Entra ID–joined, and hybrid workstations, plus Citrix and VDI environments." For details, see Avatier Login Reset.
- A call to the help desk. Avatier's service-desk line is short: "the agent verifies the caller, not the caller's phone." On the call, "The agent names a coordinate, the caller reads the answer off their printed card, and that value is spent." For associates who do have an enrolled device, Avatier Assisted Reset takes the other route: "Every challenge goes to the user — the agent only sees pass or fail." For the full caller procedure, see How to Verify Help Desk Callers with the Identity Challenge Card.
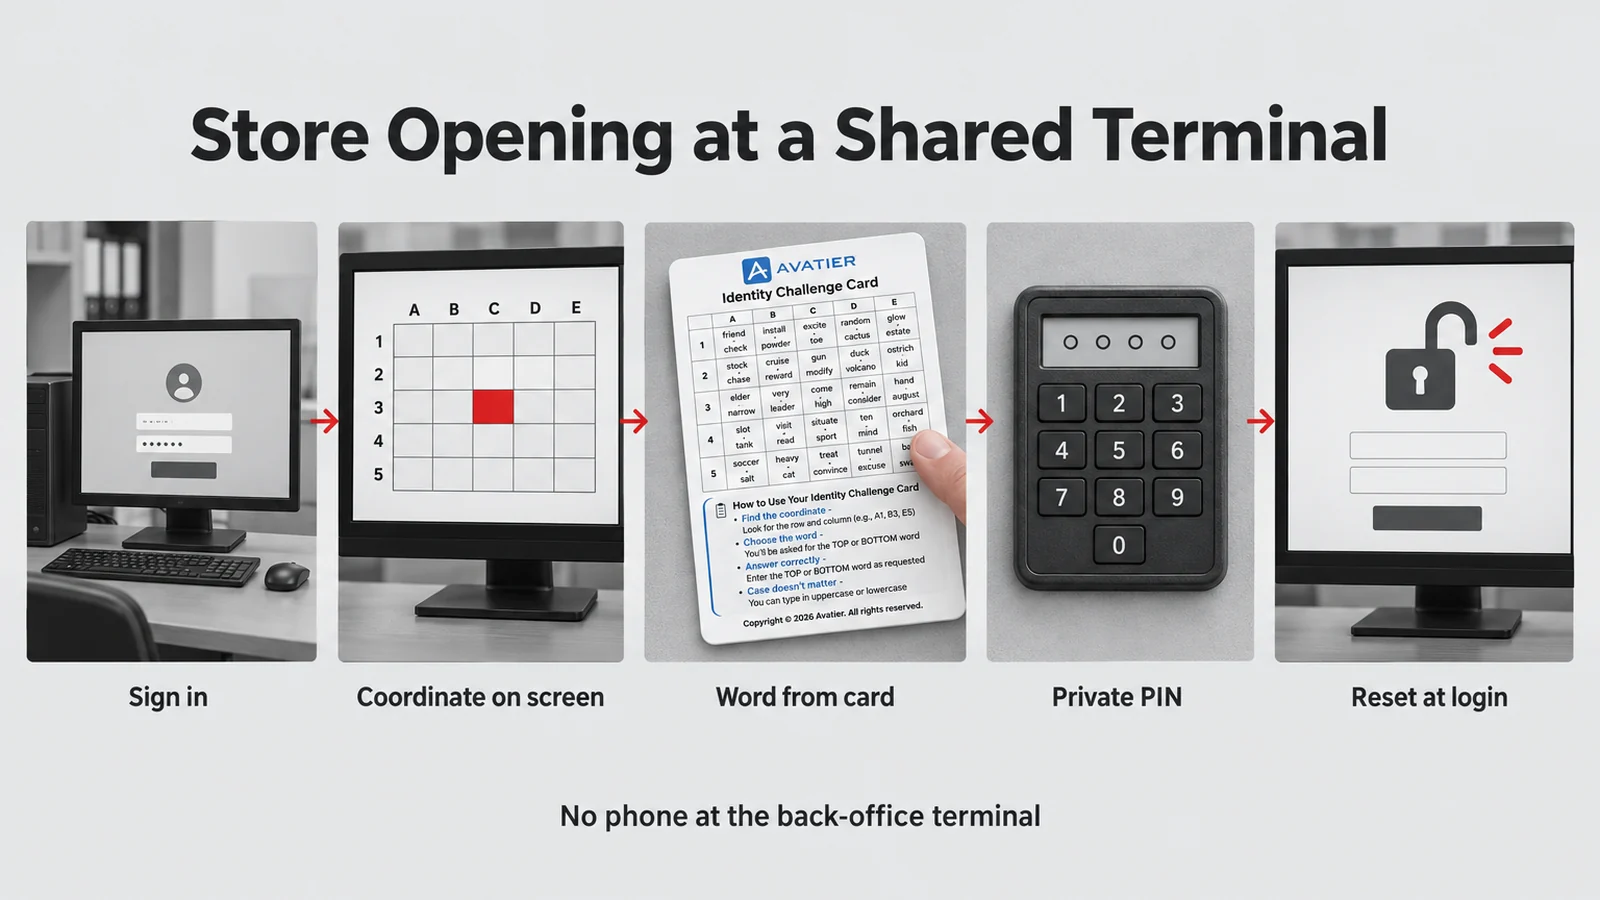 One associate at a shared back-office terminal: sign in with the card, or reset a lockout at the login screen before the doors open.
Seasonal hiring and promotions without leftover access
Avatier's HR User Provisioning page lists the seasonal scenario directly: "Businesses with recurring hiring cycles need fast onboarding, access removal and license reclamation when assignments end, and correct role-based access when workers return." Three pieces handle it:
- HR User Provisioning connects to "70+ HR and payroll systems through a single unified integration." When an associate moves up to key holder or store manager, "On a transfer or promotion, it applies the new role's access and removes what no longer fits."
- Group Automation drives membership "straight from authoritative HR attributes: title, department, location, and manager." "When someone is hired, moved, or leaves, their groups follow." Before a rule goes live, "you test it against live data and see exactly who will be added or removed."
- Cards follow governance. Avatier says "Cards are issued through the identity governance workflow you already run," and "Admins set expiry windows; users receive automated reminders." In Avatier's comparison, the card is "Printed once, reissued in seconds." As general practice, set a seasonal associate's expiry window to match the assignment. For the issuance and revocation workflow, see Issuing, Revoking and Replacing Avatier's Identity Challenge Card.
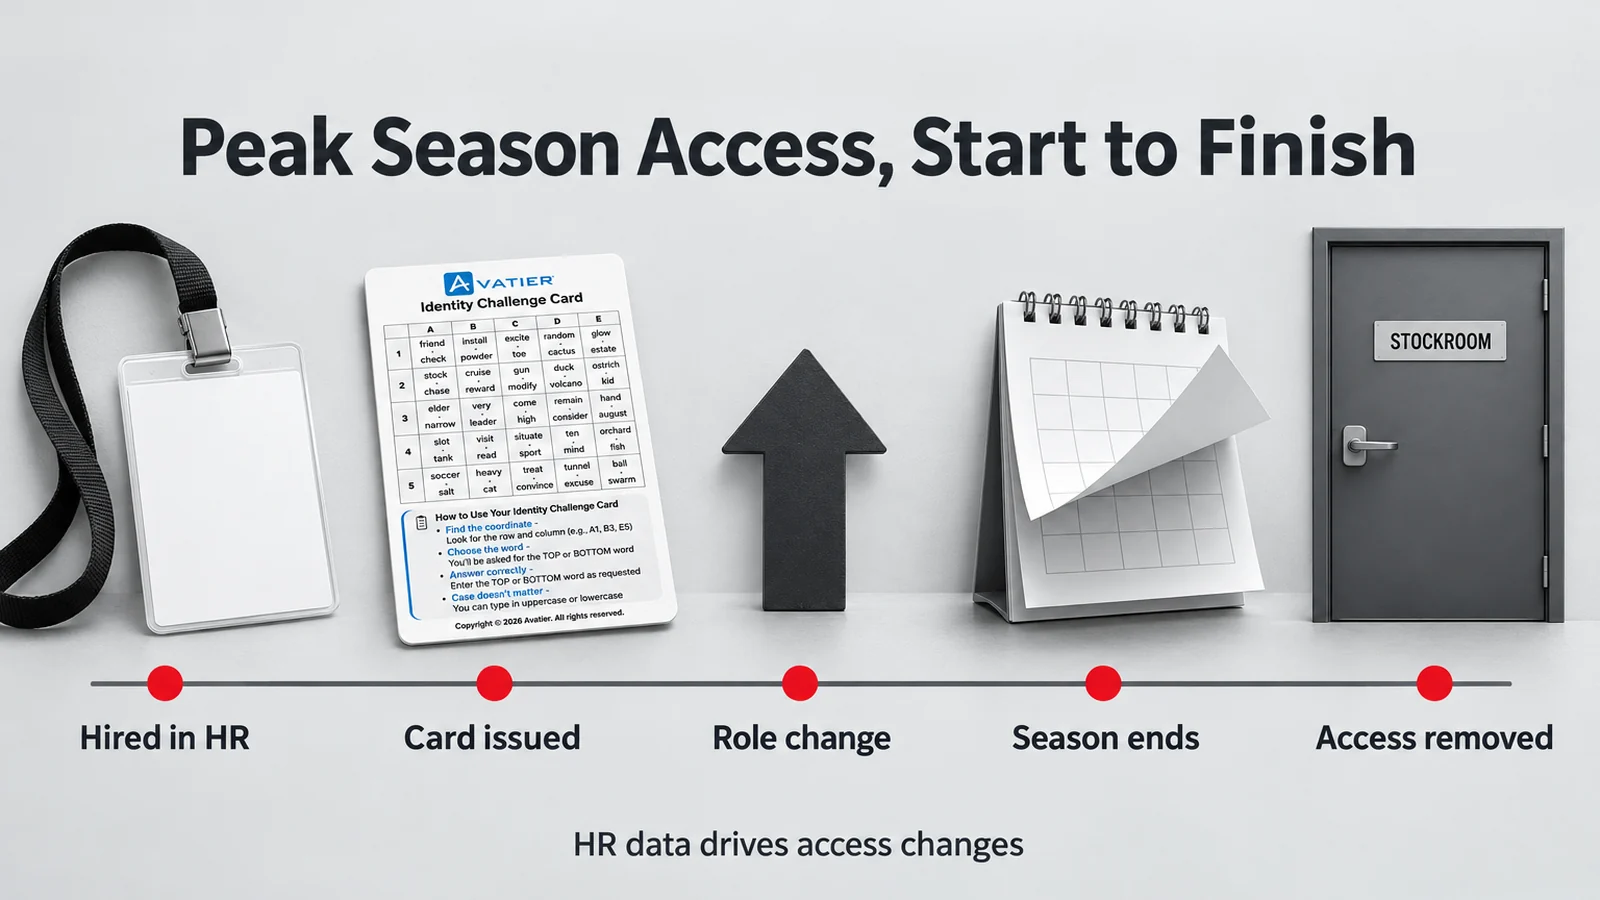 A seasonal associate's access from hire to the end of the season: HR data drives the access changes, and the card is issued through the governance workflow.
What Avatier ships toward this pattern
- Identity Challenge Card. Deviceless MFA at sign-in, at password reset and at the service desk. Avatier says the whole workforce "can be up and running in under an hour," and the card can also live in Apple Wallet, Google Wallet or Samsung Wallet "as a backup alongside the printed card." For the product, see the Identity Challenge Card.
- Login Reset. Pillar 4 of Avatier Credential Governance™: MFA-verified unlock and reset at the Windows and Mac login screen, with cached-credential updates.
- HR User Provisioning and Group Automation. Two of the five Lifecycle & Access Governance pillars, which run on the Avatier Identity Anywhere platform. Avatier says "Most customers go live in days to weeks." For the HR-driven side, see HR User Provisioning.
- Security posture. Avatier is SOC 2 Type II audited with no exceptions noted, ISO/IEC 27001:2022 certified and PCI DSS v4.0.1 compliant. For reports and certifications, see the Avatier Trust Center.
Getting started
Pricing for Avatier Identity Anywhere 2027™ is Pay Per Identity Action™: customers pay only for completed, verified, policy-compliant outcomes. Getting started is free, deployment services are included, and a 45-day money-back guarantee applies. Full terms are available in the invitation-only preview. For the platform, see the Avatier Identity Anywhere 2027™ preview. For Avatier's full product line, see avatier.com.
About the author
More from Frontline & Shared Devices
MFA for Plant Floors Without Phones: Shared Terminals, with Avatier
How to run MFA on a manufacturing plant floor where phones are banned or not issued: Avatier's printed Identity Challenge Card at shared terminals, plus outages, lockouts and role churn.
MFA for Frontline Workers Without Phones: The Identity Challenge Card
Frontline and shared-device workers can't always use a phone for MFA. How Avatier's Identity Challenge Card gives them a printed factor for login, password reset, and the service desk.
New-Hire MFA on Day One: Closing the Enrollment Gap with Avatier
A new hire needs MFA before a phone, authenticator or device is enrolled. How Avatier's Identity Challenge Card closes the first-day enrollment gap through one IGA workflow.