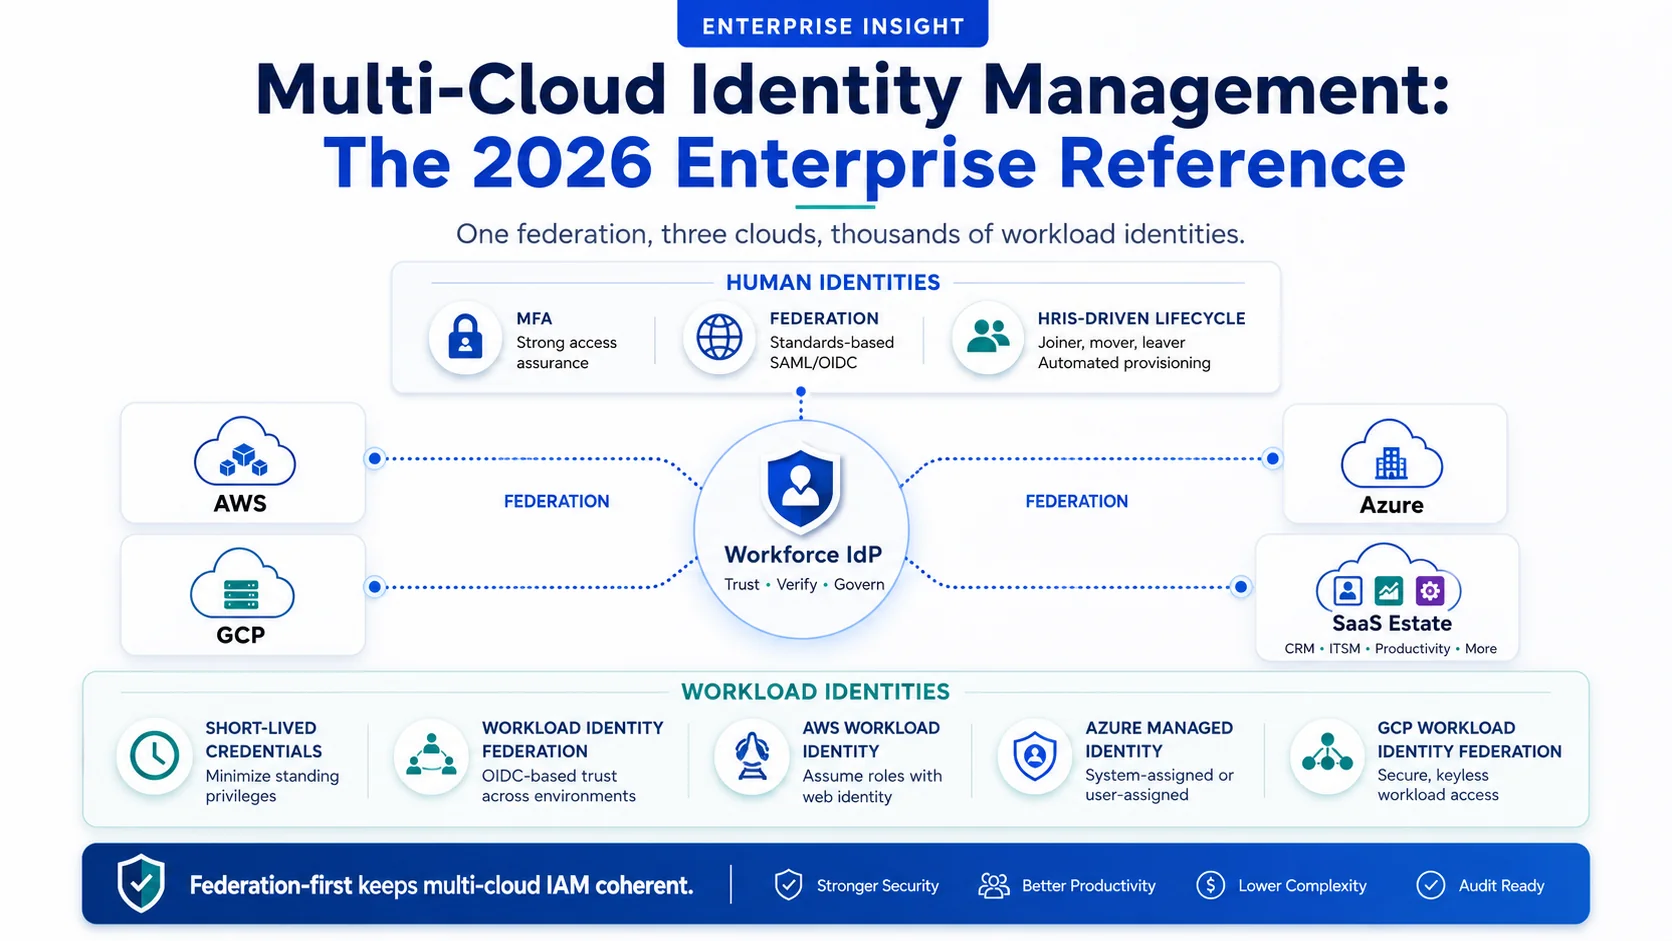
Retiring MFA Exceptions: Full-Workforce MFA with Avatier
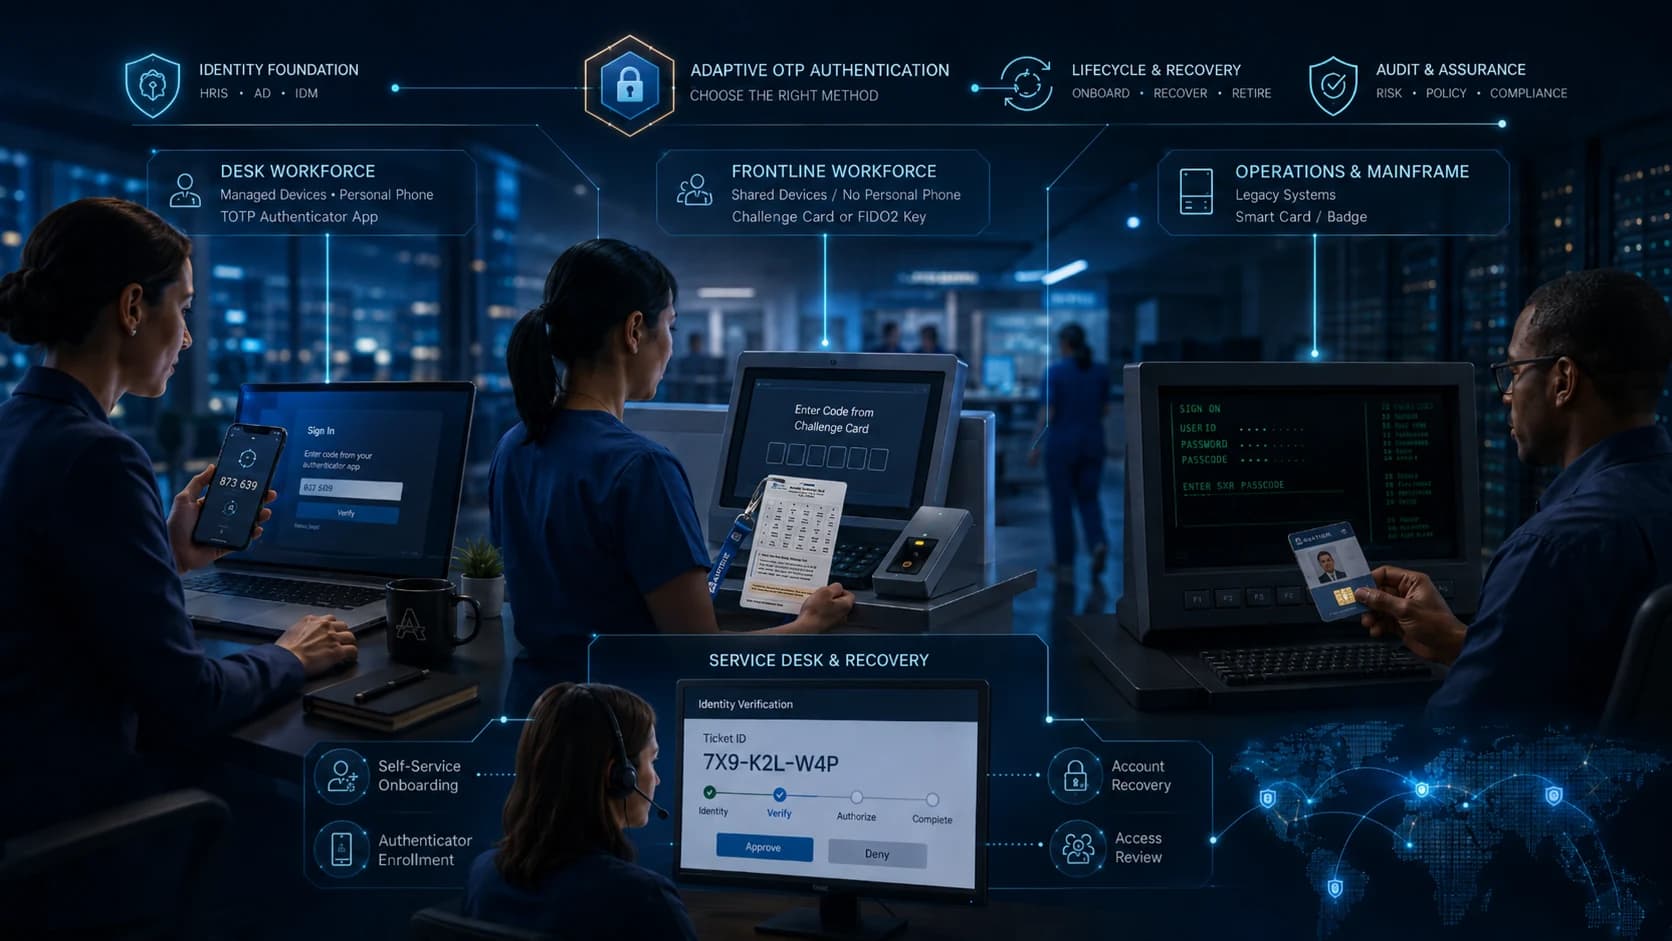
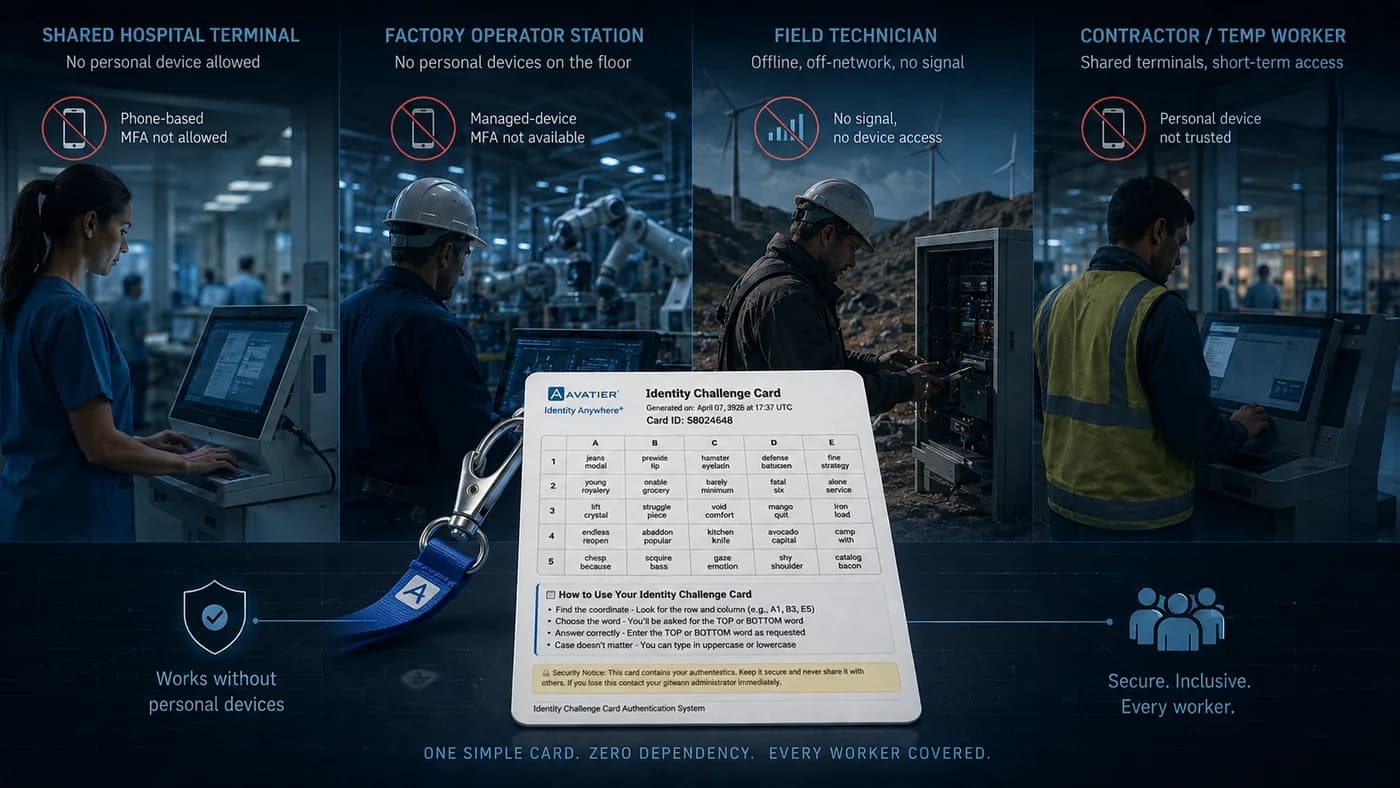
An MFA exception register lists the workers device MFA can't reach. How Avatier's Identity Challenge Card lets policy route each of them to a method, so exceptions can be retired.
Multi-factor authentication strategy, methods, and buyer's guides.
Showing 30 posts

An MFA exception register lists the workers device MFA can't reach. How Avatier's Identity Challenge Card lets policy route each of them to a method, so exceptions can be retired.

Avatier's Identity Challenge Card ships in 34 languages, including right-to-left Arabic and CJK scripts. Same card, same three-factor flow, localized for every worker.

Avatier's Identity Challenge Card can be added to Apple Wallet, Google Wallet or Samsung Wallet, alongside the printed card. When to reach for the wallet card, and when for the printed one.

How Avatier's Identity Challenge Card is issued through one IGA workflow, expires and re-enrolls by policy, and is revoked in seconds and replaced the same day when a card is lost.

What three-factor authentication is, how 3FA differs from 2FA, and how Avatier's Identity Challenge Card checks three factors: a printed grid card, a private PIN and a directory identity.

When the identity provider, MFA service or devices go down, people still have to prove who they are. A runbook for verifying, restoring and recording access with Avatier's printed card.

Air-gapped MFA for sites where phones are banned or networks don't reach. How Avatier's printed Identity Challenge Card verifies a worker locally, with no phone, no app and no network.

AI call center authentication means proving a caller is who they claim before any reset or unlock runs, whether a human agent or AI voice answers. What strong caller verification looks like.

An Identity Continuity Layer keeps authentication working when phones are lost, batteries die, or signal drops. What it is, where device MFA breaks, and how the Identity Challenge Card fills the gap.

Consent phishing lures a user to a real OAuth consent screen for a malicious app, they click Allow, and the attacker walks away with a token that grants lasting access. Because no password is stolen, MFA never fires. The 2026 reference on how the illicit consent grant works and the app-governance defenses that actually stop it.

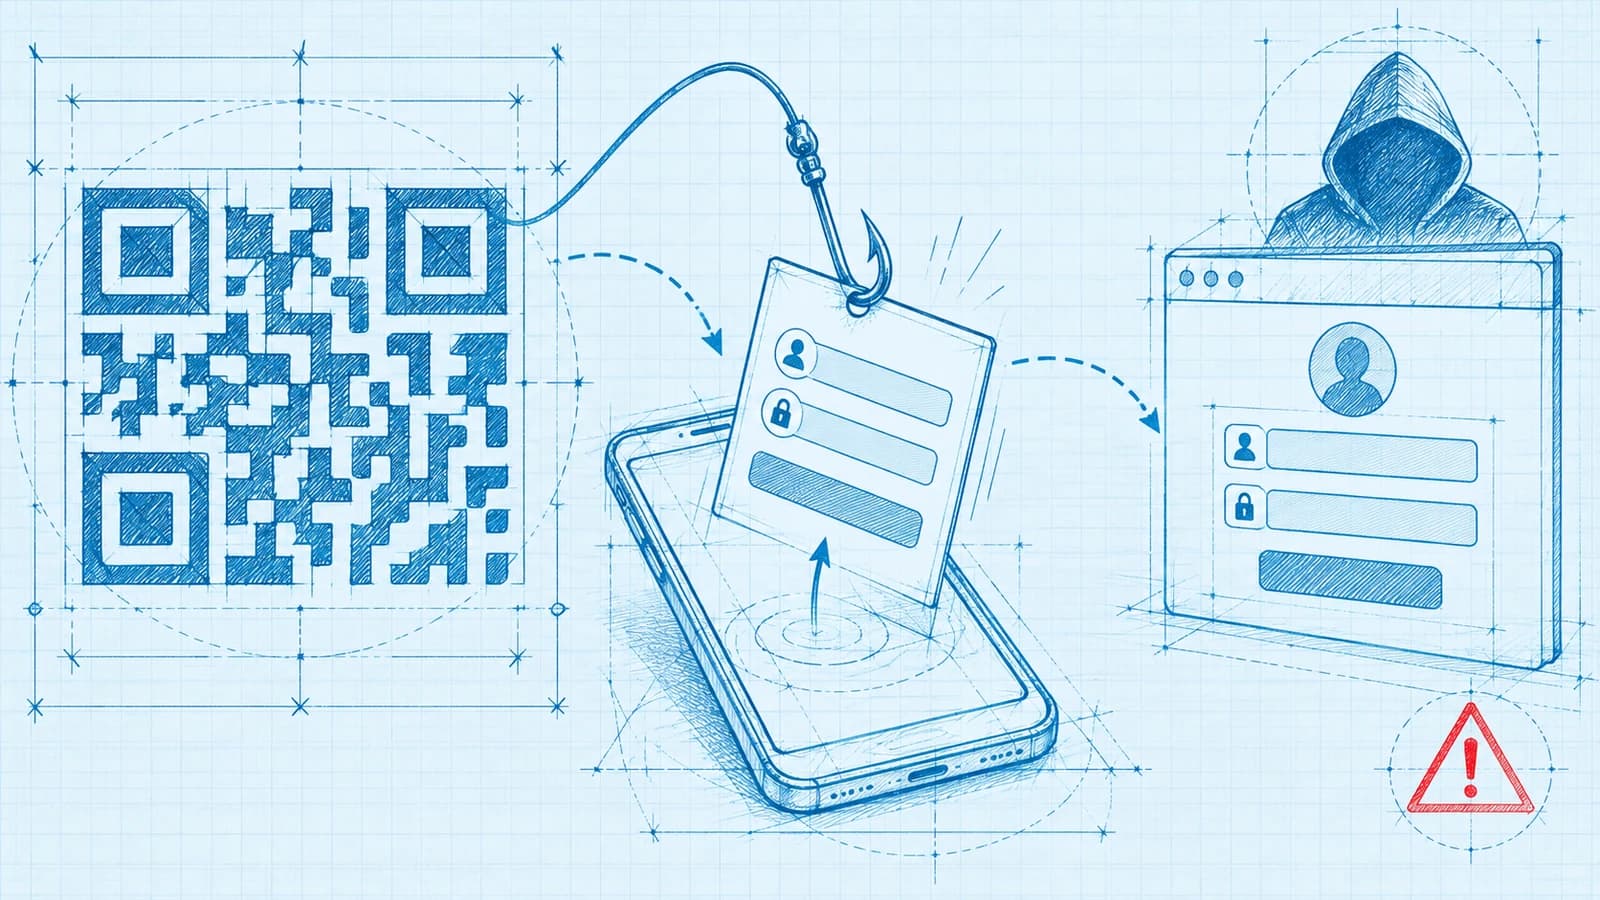
Quishing hides a malicious URL inside a QR code, slips past email link scanners, and moves the victim onto a personal phone where the fake login is hard to inspect. The 2026 reference on how the attack runs and the phishing-resistant defenses that actually stop it.

Credential stuffing replays username and password pairs leaked from other breaches against your login, at automated scale, until reused passwords hit. The 2026 reference on how the attack chain works, why it differs from brute force and password spraying, and the layered defenses that actually stop it.

Step-up authentication keeps baseline login light for routine work and demands fresh, stronger verification the moment an action turns sensitive. The 2026 reference on what triggers a step-up, how users complete one, and how it differs from adaptive authentication.

Attackers get past MFA without breaking the cryptography — SIM swap, adversary-in-the-middle, session and token theft, MFA fatigue, and consent phishing. How the AiTM bypass chains, and the defenses that actually close it.

Weak OTP fails at four specific points — SIM swap, real-time phishing relay, SS7 interception, and MFA fatigue — and every one of them is a known, repeatable attacker technique in 2026.

Multi-factor authentication only works when the factors are genuinely different — this 2026 reference clears up what counts as a real factor and what advanced MFA actually means.

OTP does not stop every attack, but it reliably defeats credential stuffing, password-spray, basic brute force, and stolen-password reuse from unrelated breaches. The 2026 breach-prevention case for OTP — the attack chains it breaks, the ones it doesn't, and how to deploy it so the prevention benefit actually lands.

OTP fails less on cryptography than on deliverability, SIM-swap and phishing exposure, UX friction, and compliance. The real challenges of one-time passwords in 2026 — and how to implement OTP well.

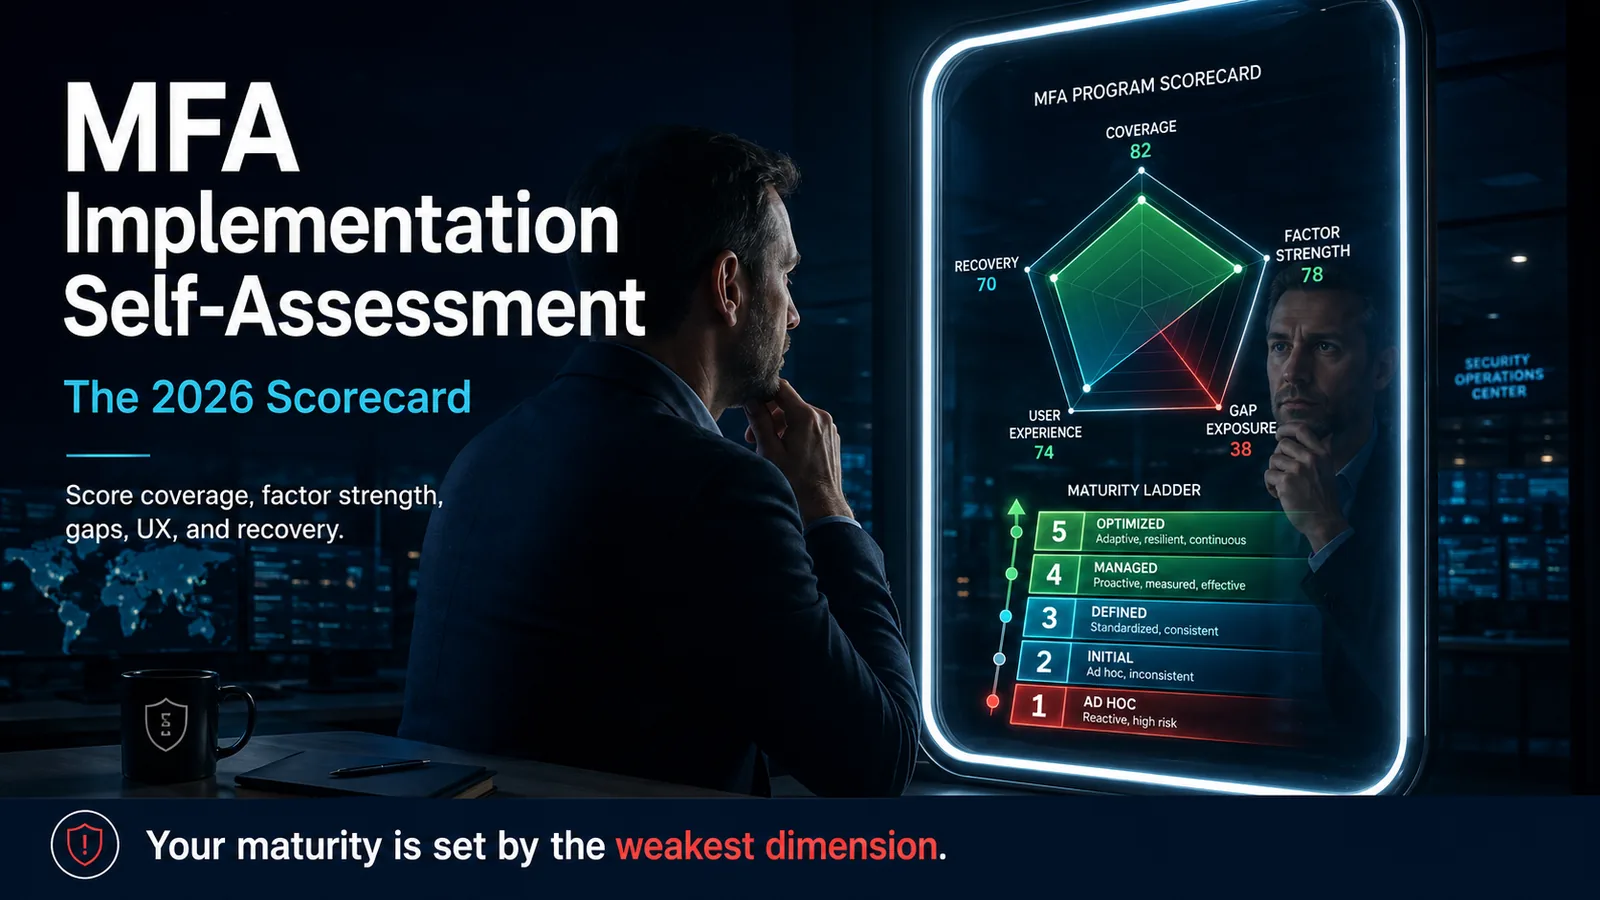
How to assess your own enterprise MFA implementation in 2026 — a scored self-assessment across coverage, factor strength, gaps, user experience, and recovery on a five-level maturity ladder.

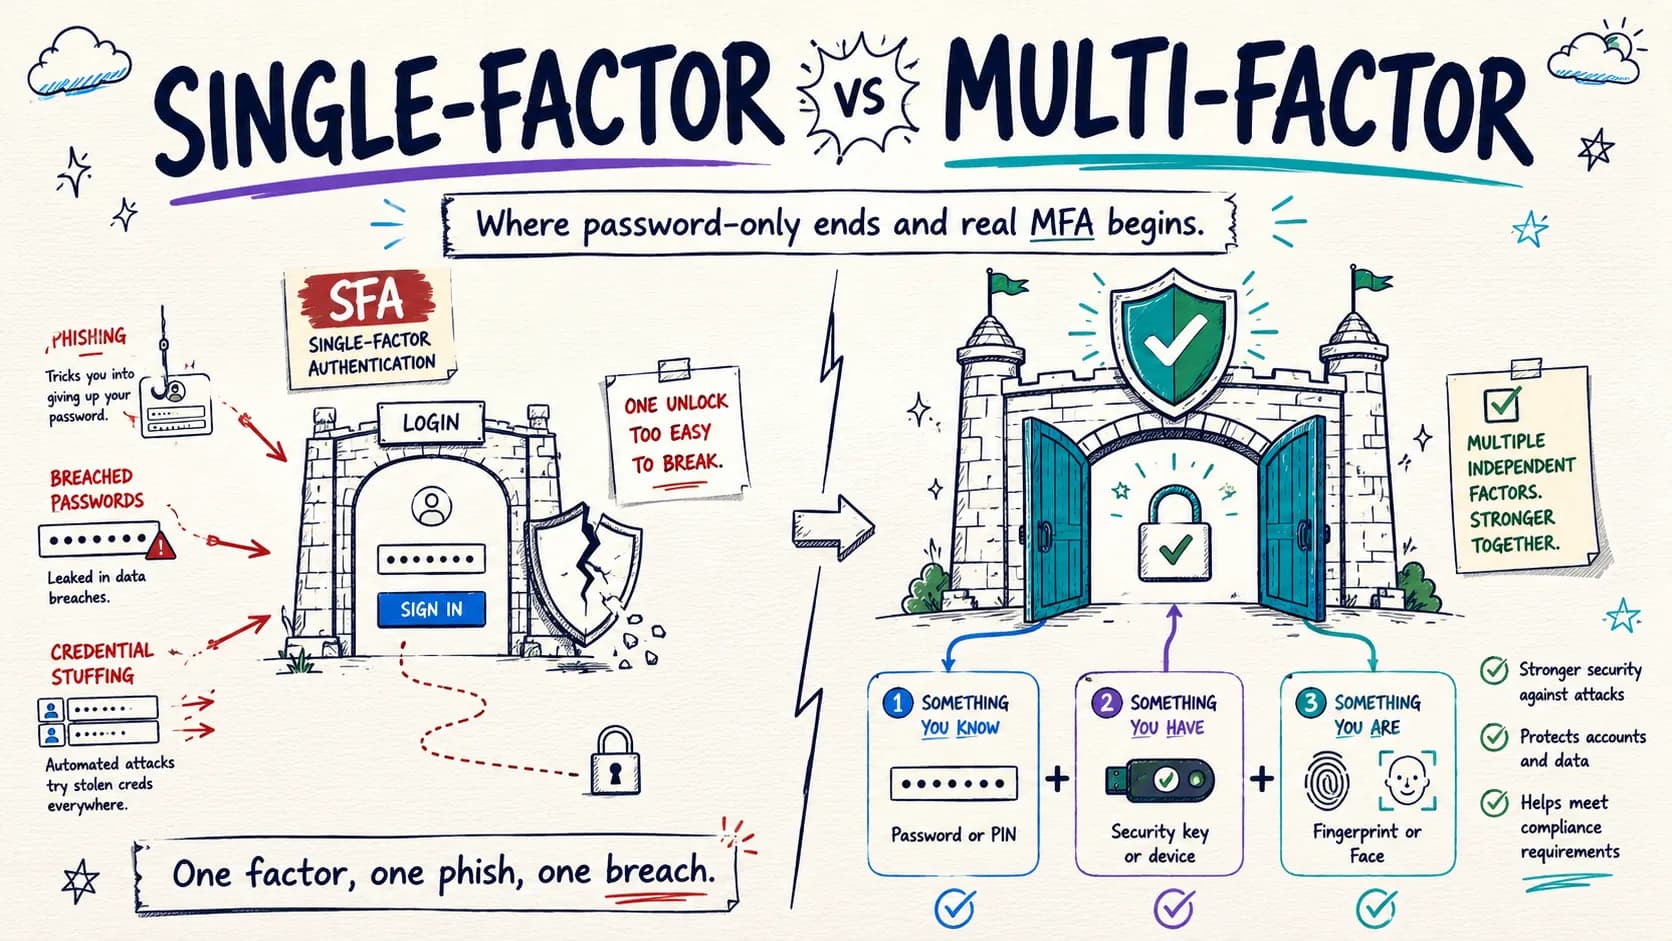
Single-factor authentication still runs most login events on earth, and most of the advice about it is a strawman. The 2026 reference on what SFA actually is, where it remains defensible, why factor independence decides whether you really have MFA, and the failure ladder from password-only to phishing-resistant FIDO2.

One-time passwords fail in specific, patterned ways at enterprise scale — SMS interception through SS7 and SIM-swap, TOTP time drift and device loss, push-notification MFA fatigue, hardware token failures, and the recovery-channel gap that determines whether the failure produces a help desk ticket or a security incident. The 2026 enterprise reference on how OTP actually fails in production and what to deploy instead.

Mobile biometric authentication has quietly become the primary phishing-resistant credential class for enterprise workforce authentication. The 2026 enterprise reference on what's actually happening on modern mobile devices, how platform passkeys and biometric unlock compose into FIDO2 authentication, and where mobile biometric MFA still needs step-up to a hardware key or deviceless credential.

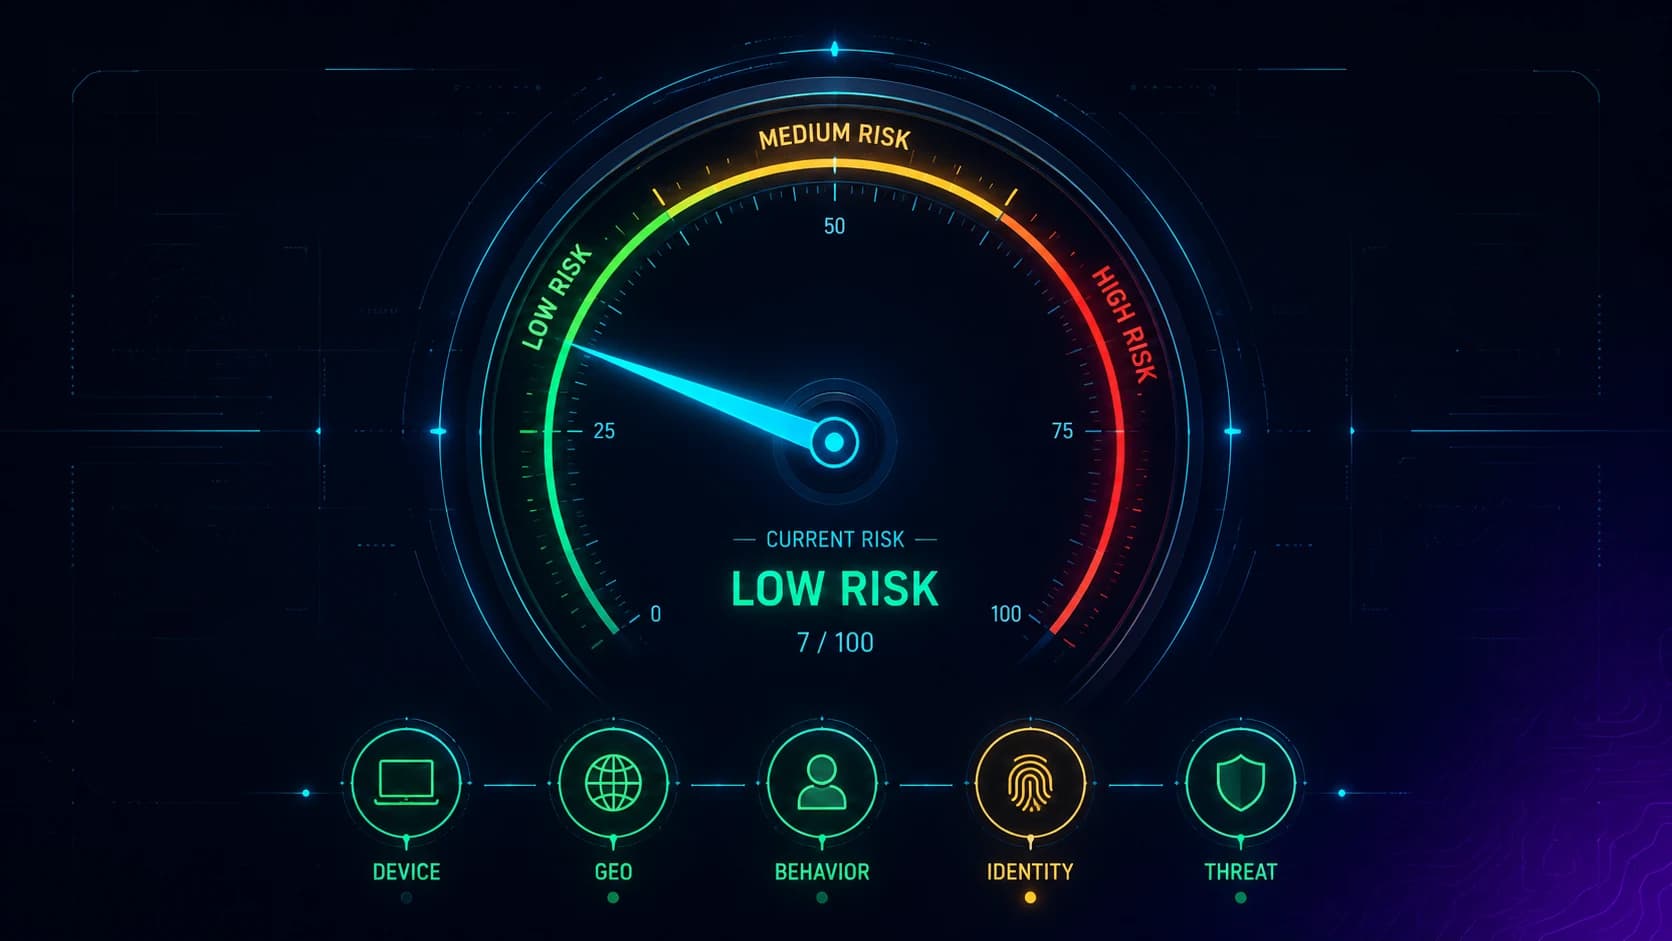
Adaptive authentication evaluates risk signals at every session and adjusts the authentication requirement to match — stronger MFA when risk is high, frictionless access when risk is low. The 2026 enterprise reference on the signals that actually matter, the architecture that composes risk with phishing-resistant MFA, and where adaptive deployments break.

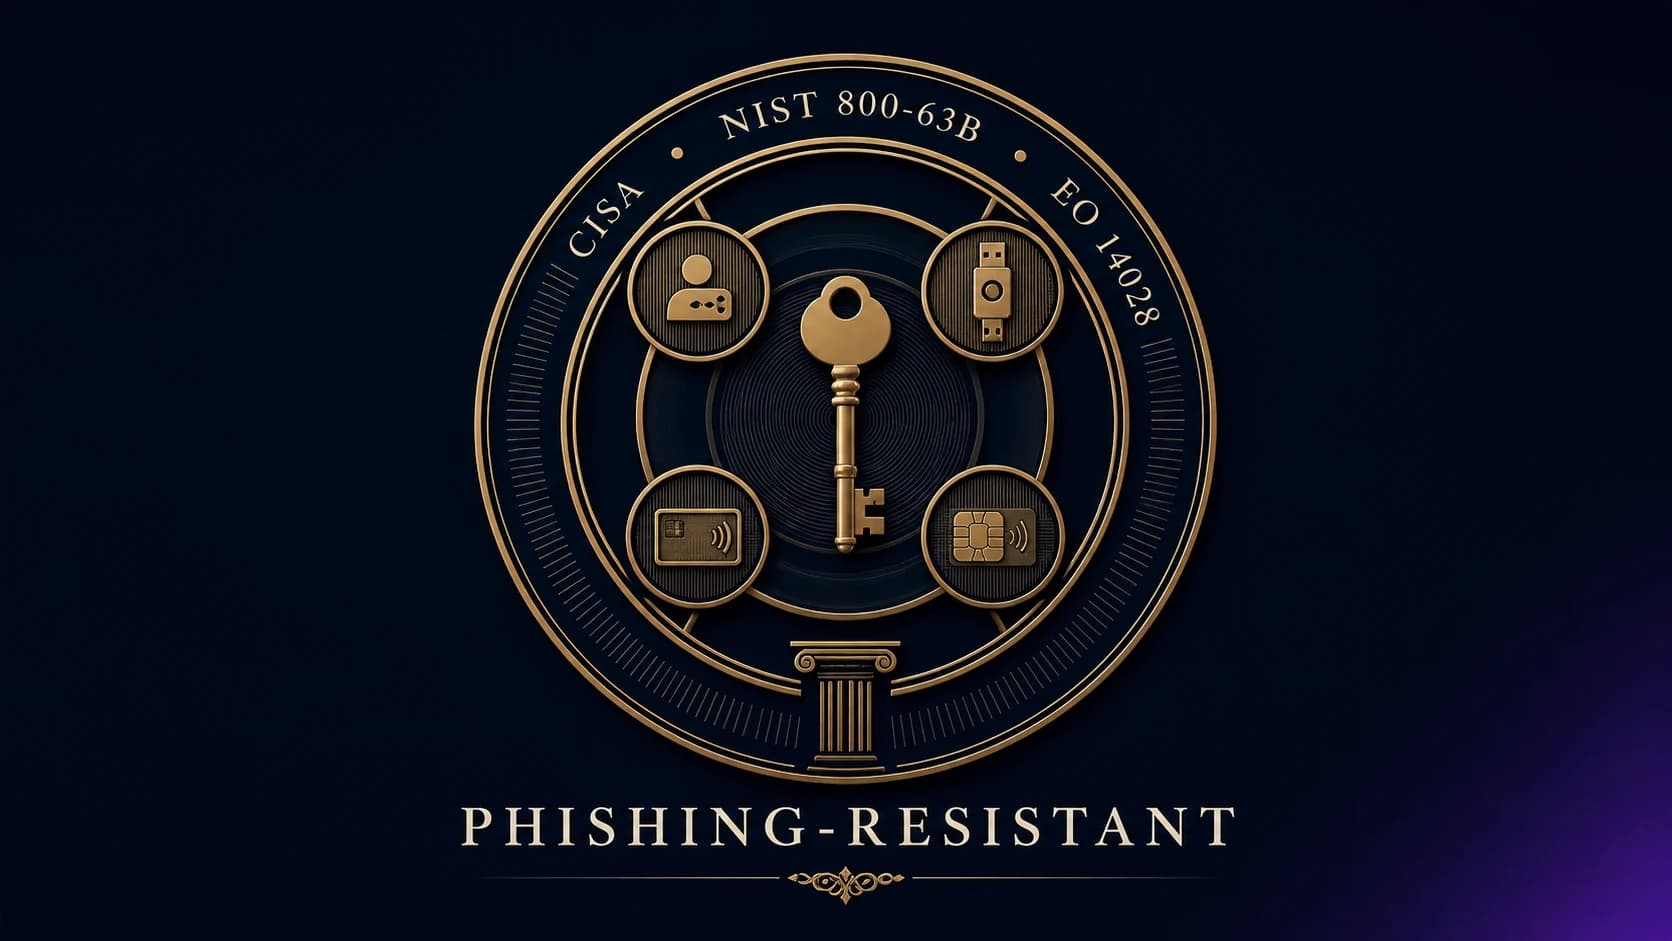
Phishing-resistant MFA is the term CISA, NIST 800-63B Rev. 4, and Executive Order 14028 use for the authentication category that survives the attack patterns that defeated SMS, OTP, and push-approval MFA. The 2026 enterprise reference on what qualifies, what doesn't, and the deployment architecture across mixed workforces.

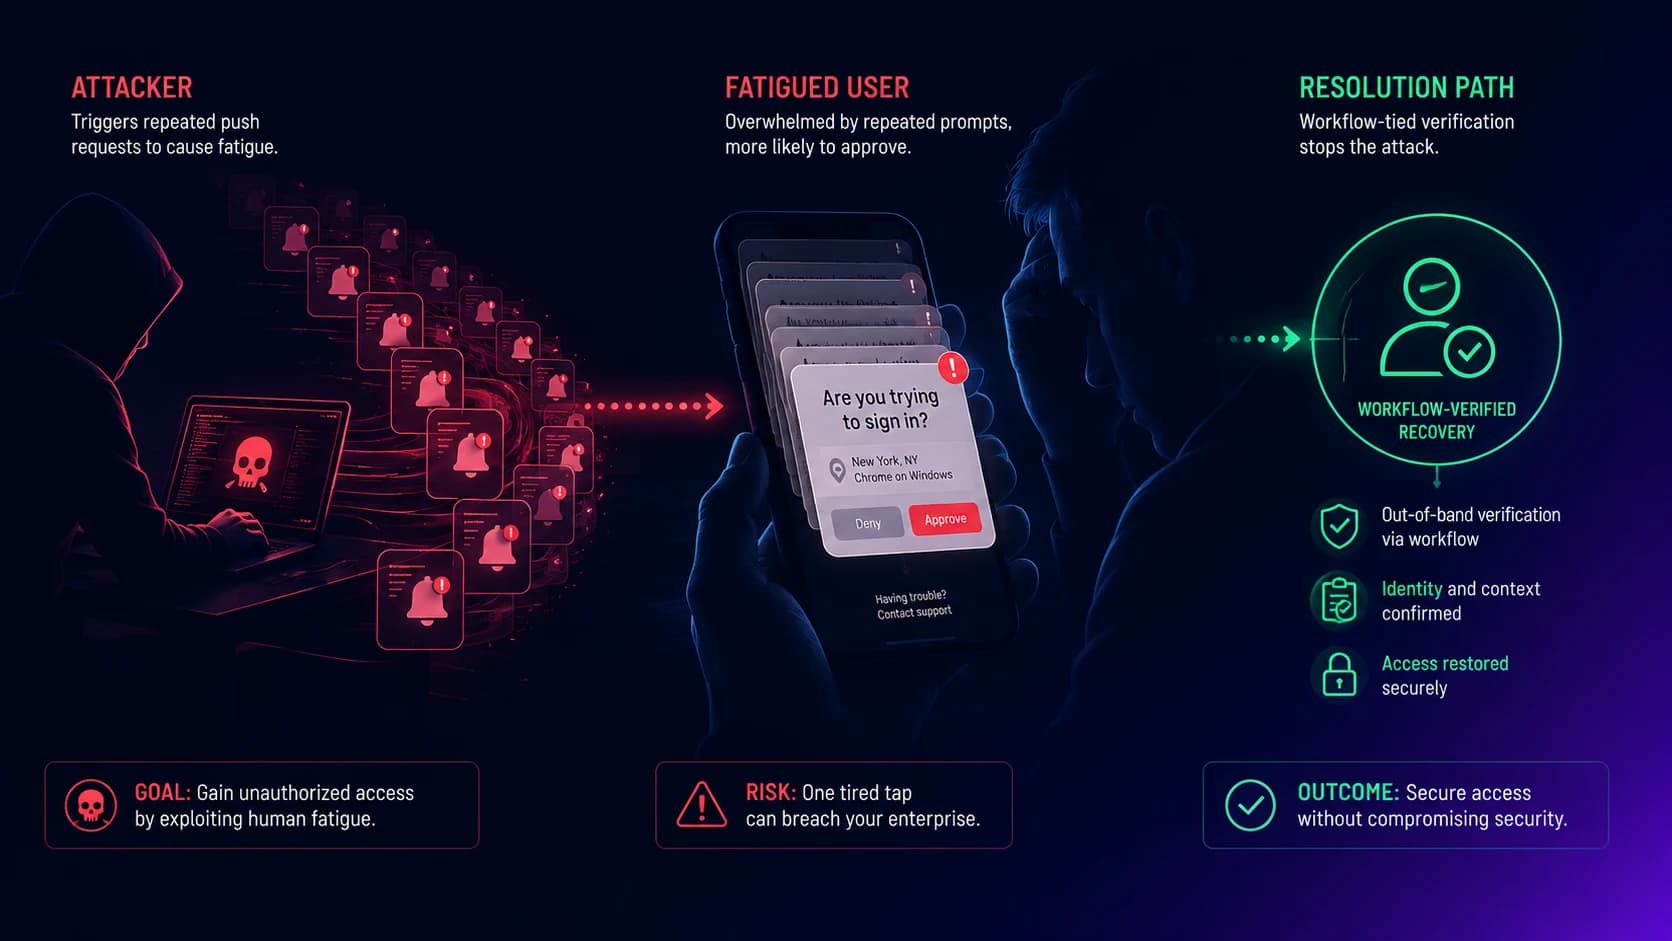
Push-bombing and MFA fatigue attacks defeat MFA by exhausting the user, not the cryptography. The 2026 defense patterns — number matching, push throttling, phishing-resistant migration, and the architecture that survives the attack vector that took down Uber, Cisco, and a long list of enterprises since 2022.

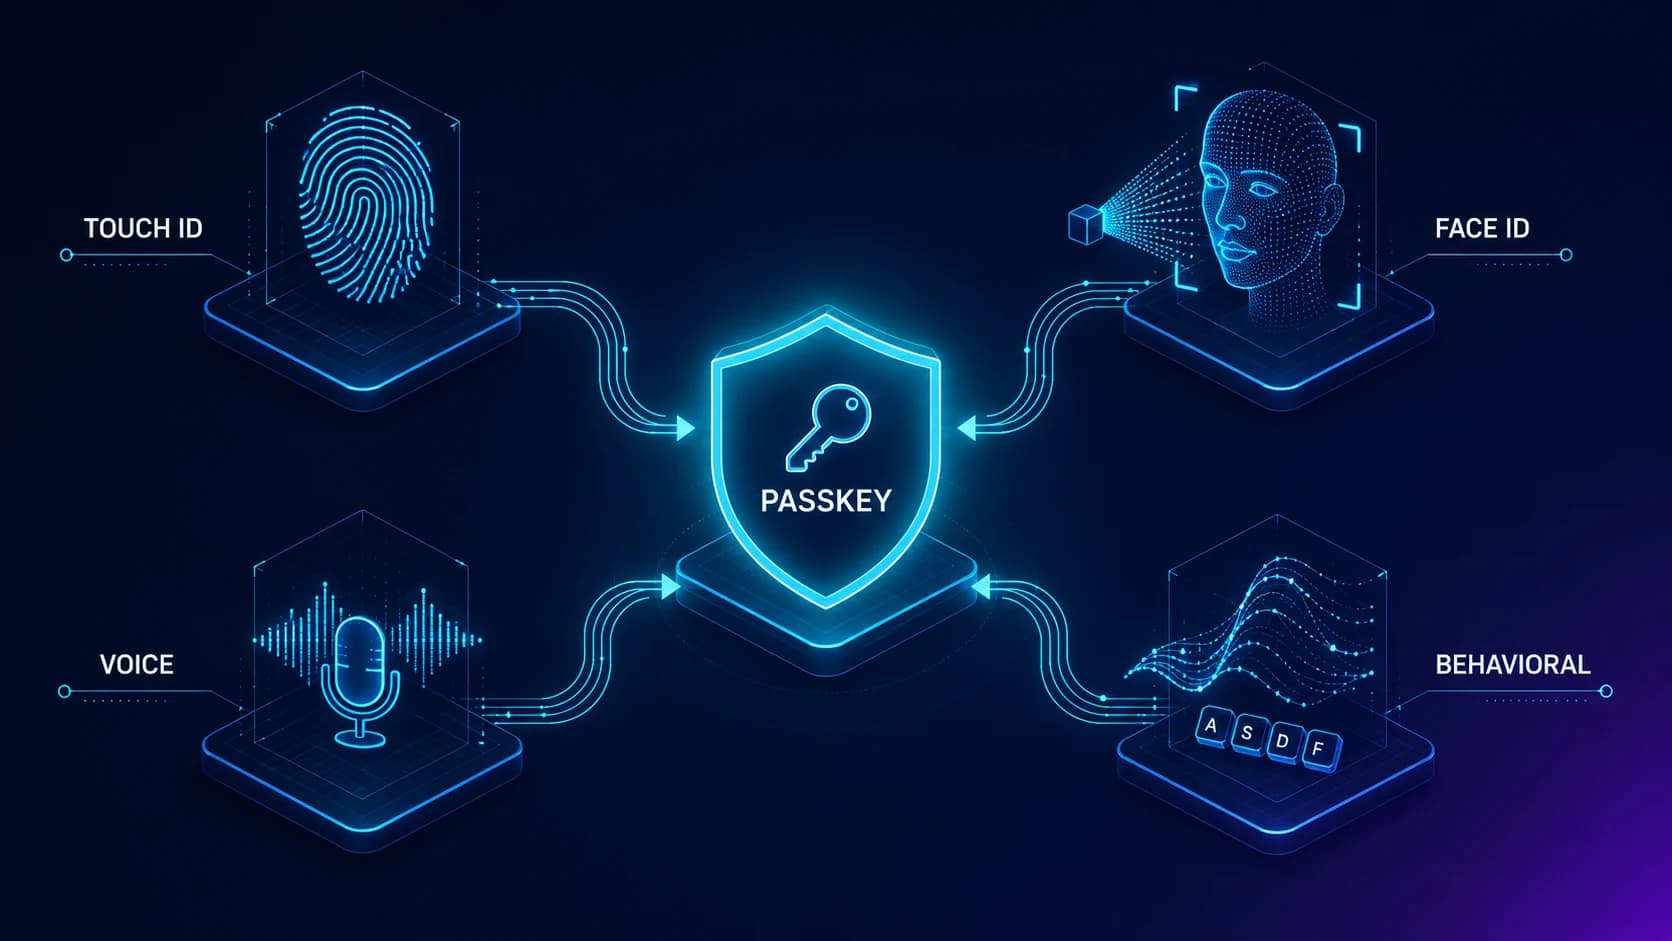
Biometric authentication is no longer a Hollywood prop — it's the dominant unlock mechanism for every passkey deployed in 2026. The honest enterprise guide to which biometrics are production-grade, which are still demo-only, and how biometrics fit into the workforce MFA architecture.

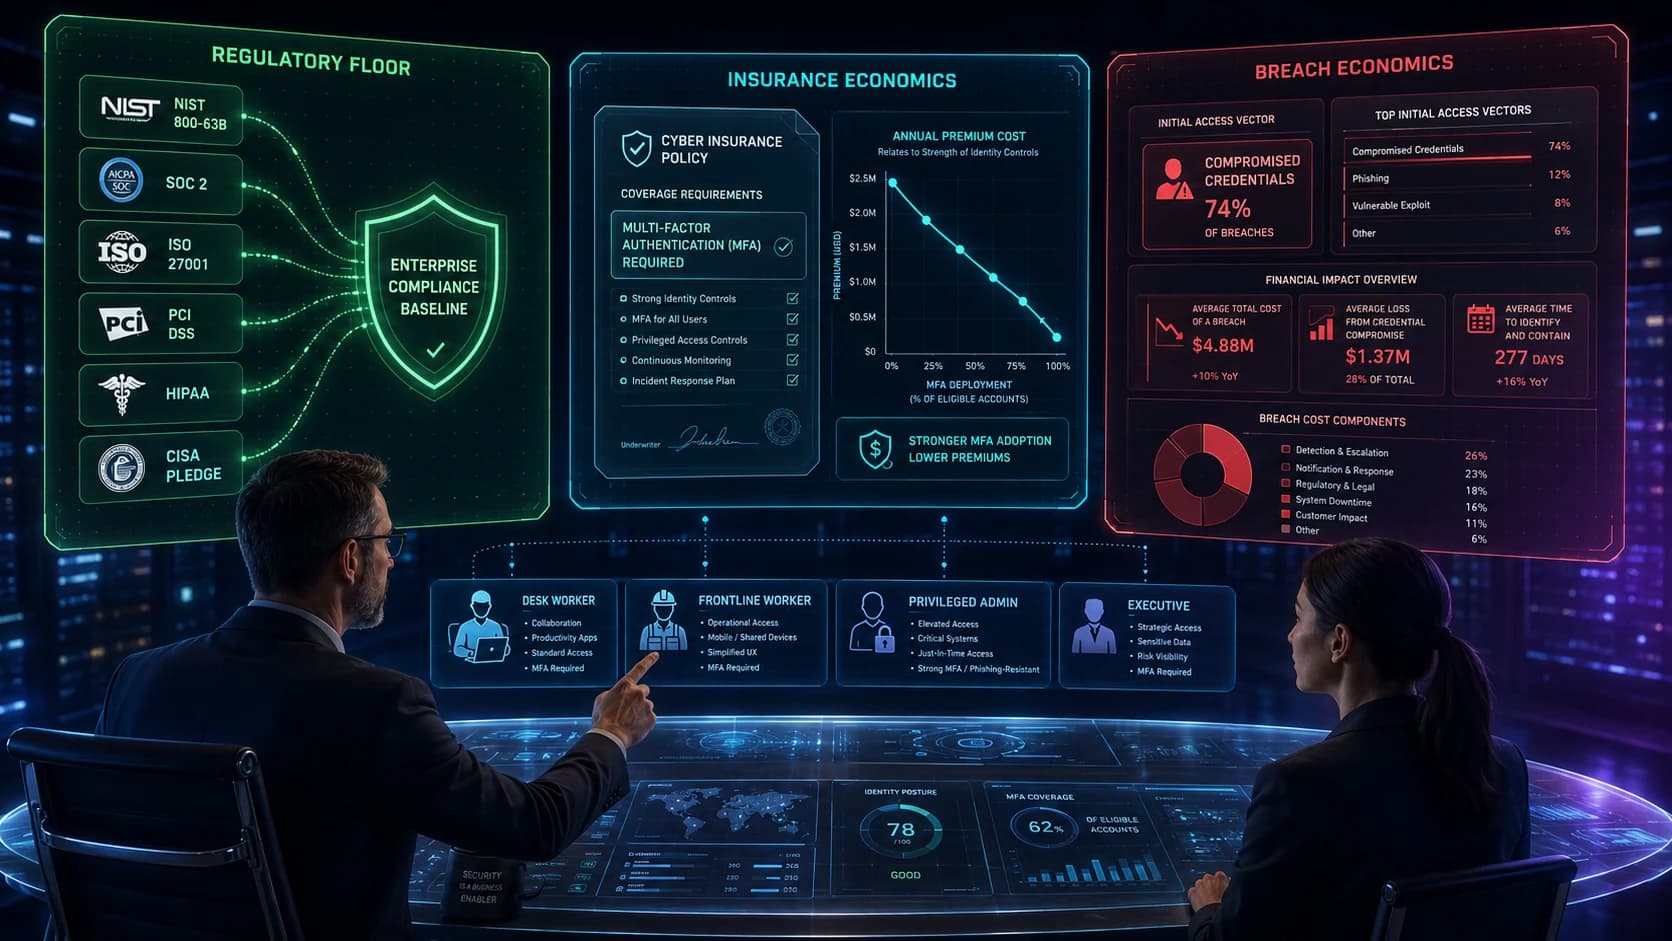
The real reasons enterprises deploy MFA — what's changed since 2024, what Storm-2949 taught us about the recovery channel, and how to evaluate whether your MFA architecture is actually doing the job.

How to scale OTP across an enterprise in 2026 — channel selection, recovery design, workforce segmentation, and where OTP belongs in a phishing-resistant architecture.

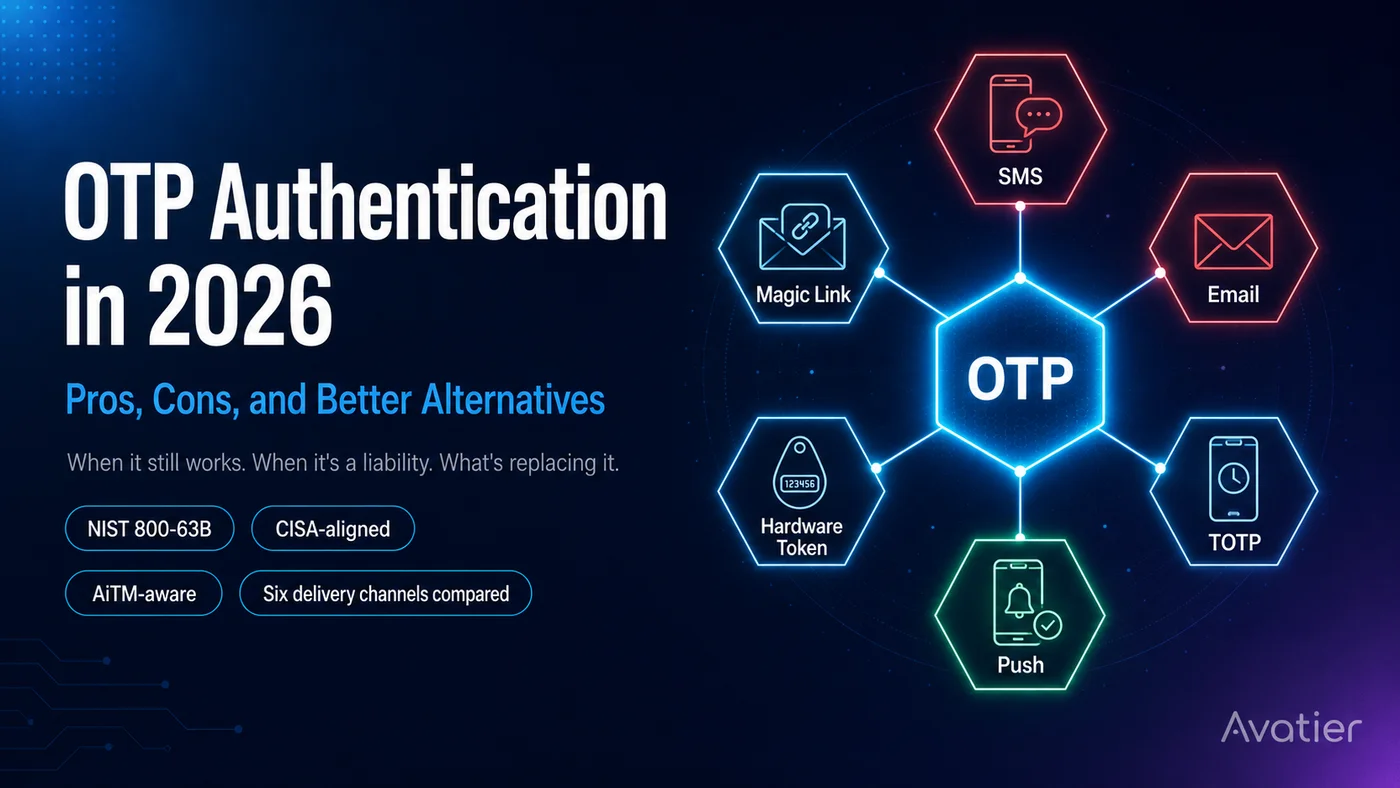
When one-time passwords still hold up in 2026, when they don't, and the phishing-resistant alternatives that have replaced them for high-impact use cases.

What the Stryker attack revealed about device-dependent MFA — and what phishing-resistant authentication actually means in an era of AiTM session theft.